جهت دسترسی به کاربرگه ی زیر، از این لینک استفاده کنید.
http://localhost/handle/Hannan/617
نمایش کامل اطلاعات کتابشناختی
| فیلد DublinCore | مقدار | زبان |
|---|---|---|
| dc.contributor.author | Lahiri, Shuvendu K. ; | en_US |
| dc.contributor.author | Wang, Chao. ; | en_US |
| dc.date.accessioned | 2013 | en_US |
| dc.date.accessioned | 2020-05-17T08:19:37Z | - |
| dc.date.available | 2020-05-17T08:19:37Z | - |
| dc.date.issued | 2018 | en_US |
| dc.identifier.isbn | 9783030010904 ; | en_US |
| dc.identifier.isbn | 9783030010898 (print) ; | en_US |
| dc.identifier.uri | http://localhost/handle/Hannan/617 | - |
| dc.description | SpringerLink (Online service) ; | en_US |
| dc.description | en_US | |
| dc.description | en_US | |
| dc.description | 005.1 ; 23 ; | en_US |
| dc.description | Printed edition: ; 9783030010898. ; | en_US |
| dc.description | en_US | |
| dc.description | en_US | |
| dc.description.abstract | This book constitutes the refereed proceedings of the 24th International Symposium on Automated Technology for Verification and Analysis, ATVA 2018, held in Los Angeles, CA, USA in October 2018. The 27 full papers presented together with 5 short papers and 3 invited talks were carefully reviewed and selected from 82 submissions. The symposium is dedicated to the promotion of research on theoretical and practical aspects of automated analysis, verification and synthesis by providing a forum for interaction between the regional and the international research communities and industry in the field. ; | en_US |
| dc.description.statementofresponsibility | edited by Shuvendu K. Lahiri, Chao Wang. | en_US |
| dc.description.tableofcontents | Formal Methods -- Verification -- Program Synthesis -- Model Checking -- Theorem Proving -- Software Verification -- SAT Solver -- SMT Solver -- Automaton Logic. ; | en_US |
| dc.format.extent | XIII, 560 p. 133 illus. ; online resource. ; | en_US |
| dc.publisher | Springer International Publishing : | en_US |
| dc.publisher | Imprint: Springer, | en_US |
| dc.relation.ispartofseries | Lecture Notes in Computer Science, ; 0302-9743 ; ; 11138. ; | en_US |
| dc.relation.ispartofseries | Lecture Notes in Computer Science, ; 0302-9743 ; ; 11138. ; | en_US |
| dc.relation.haspart | 9783030010898.pdf | en_US |
| dc.subject | Computer Science | en_US |
| dc.subject | Software Engineering | en_US |
| dc.subject | Programming Languages and Electronic Computers | en_US |
| dc.subject | Computer Security | en_US |
| dc.subject | Computer logic. ; | en_US |
| dc.subject | Mathematical logic. ; | en_US |
| dc.subject | Computer simulation. ; | en_US |
| dc.subject | Computer Science | en_US |
| dc.subject | Software Engineering | en_US |
| dc.subject | Programming Languages and Compilers and Interpreters | en_US |
| dc.subject | Systems and Data Security | en_US |
| dc.subject | Simulation and Modeling. ; | en_US |
| dc.subject | Logics and Meanings of Programs. ; | en_US |
| dc.subject | Mathematical Logic and Formal Languages. ; | en_US |
| dc.subject.lcc | QA76.758 ; | en_US |
| dc.title | Automated Technology for Verification and Analysis | en_US |
| dc.title.alternative | 16th International Symposium, ATVA 2018, Los Angeles, CA, USA, October 7-10, 2018, Proceedings / | en_US |
| dc.type | Book | en_US |
| dc.publisher.place | Cham : | en_US |
| مجموعه(های): | مدیریت فناوری اطلاعات | |
پیوست های این کاربرگه
| فایل | توضیحات | اندازه | فرمت | |
|---|---|---|---|---|
| 9783030010898.pdf | 19.14 MB | Adobe PDF | 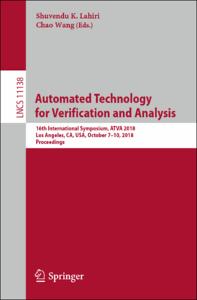 مشاهده فایل |
نمایش کامل اطلاعات کتابشناختی
| فیلد DublinCore | مقدار | زبان |
|---|---|---|
| dc.contributor.author | Lahiri, Shuvendu K. ; | en_US |
| dc.contributor.author | Wang, Chao. ; | en_US |
| dc.date.accessioned | 2013 | en_US |
| dc.date.accessioned | 2020-05-17T08:19:37Z | - |
| dc.date.available | 2020-05-17T08:19:37Z | - |
| dc.date.issued | 2018 | en_US |
| dc.identifier.isbn | 9783030010904 ; | en_US |
| dc.identifier.isbn | 9783030010898 (print) ; | en_US |
| dc.identifier.uri | http://localhost/handle/Hannan/617 | - |
| dc.description | SpringerLink (Online service) ; | en_US |
| dc.description | en_US | |
| dc.description | en_US | |
| dc.description | 005.1 ; 23 ; | en_US |
| dc.description | Printed edition: ; 9783030010898. ; | en_US |
| dc.description | en_US | |
| dc.description | en_US | |
| dc.description.abstract | This book constitutes the refereed proceedings of the 24th International Symposium on Automated Technology for Verification and Analysis, ATVA 2018, held in Los Angeles, CA, USA in October 2018. The 27 full papers presented together with 5 short papers and 3 invited talks were carefully reviewed and selected from 82 submissions. The symposium is dedicated to the promotion of research on theoretical and practical aspects of automated analysis, verification and synthesis by providing a forum for interaction between the regional and the international research communities and industry in the field. ; | en_US |
| dc.description.statementofresponsibility | edited by Shuvendu K. Lahiri, Chao Wang. | en_US |
| dc.description.tableofcontents | Formal Methods -- Verification -- Program Synthesis -- Model Checking -- Theorem Proving -- Software Verification -- SAT Solver -- SMT Solver -- Automaton Logic. ; | en_US |
| dc.format.extent | XIII, 560 p. 133 illus. ; online resource. ; | en_US |
| dc.publisher | Springer International Publishing : | en_US |
| dc.publisher | Imprint: Springer, | en_US |
| dc.relation.ispartofseries | Lecture Notes in Computer Science, ; 0302-9743 ; ; 11138. ; | en_US |
| dc.relation.ispartofseries | Lecture Notes in Computer Science, ; 0302-9743 ; ; 11138. ; | en_US |
| dc.relation.haspart | 9783030010898.pdf | en_US |
| dc.subject | Computer Science | en_US |
| dc.subject | Software Engineering | en_US |
| dc.subject | Programming Languages and Electronic Computers | en_US |
| dc.subject | Computer Security | en_US |
| dc.subject | Computer logic. ; | en_US |
| dc.subject | Mathematical logic. ; | en_US |
| dc.subject | Computer simulation. ; | en_US |
| dc.subject | Computer Science | en_US |
| dc.subject | Software Engineering | en_US |
| dc.subject | Programming Languages and Compilers and Interpreters | en_US |
| dc.subject | Systems and Data Security | en_US |
| dc.subject | Simulation and Modeling. ; | en_US |
| dc.subject | Logics and Meanings of Programs. ; | en_US |
| dc.subject | Mathematical Logic and Formal Languages. ; | en_US |
| dc.subject.lcc | QA76.758 ; | en_US |
| dc.title | Automated Technology for Verification and Analysis | en_US |
| dc.title.alternative | 16th International Symposium, ATVA 2018, Los Angeles, CA, USA, October 7-10, 2018, Proceedings / | en_US |
| dc.type | Book | en_US |
| dc.publisher.place | Cham : | en_US |
| مجموعه(های): | مدیریت فناوری اطلاعات | |
پیوست های این کاربرگه
| فایل | توضیحات | اندازه | فرمت | |
|---|---|---|---|---|
| 9783030010898.pdf | 19.14 MB | Adobe PDF | مشاهده فایل |
نمایش کامل اطلاعات کتابشناختی
| فیلد DublinCore | مقدار | زبان |
|---|---|---|
| dc.contributor.author | Lahiri, Shuvendu K. ; | en_US |
| dc.contributor.author | Wang, Chao. ; | en_US |
| dc.date.accessioned | 2013 | en_US |
| dc.date.accessioned | 2020-05-17T08:19:37Z | - |
| dc.date.available | 2020-05-17T08:19:37Z | - |
| dc.date.issued | 2018 | en_US |
| dc.identifier.isbn | 9783030010904 ; | en_US |
| dc.identifier.isbn | 9783030010898 (print) ; | en_US |
| dc.identifier.uri | http://localhost/handle/Hannan/617 | - |
| dc.description | SpringerLink (Online service) ; | en_US |
| dc.description | en_US | |
| dc.description | en_US | |
| dc.description | 005.1 ; 23 ; | en_US |
| dc.description | Printed edition: ; 9783030010898. ; | en_US |
| dc.description | en_US | |
| dc.description | en_US | |
| dc.description.abstract | This book constitutes the refereed proceedings of the 24th International Symposium on Automated Technology for Verification and Analysis, ATVA 2018, held in Los Angeles, CA, USA in October 2018. The 27 full papers presented together with 5 short papers and 3 invited talks were carefully reviewed and selected from 82 submissions. The symposium is dedicated to the promotion of research on theoretical and practical aspects of automated analysis, verification and synthesis by providing a forum for interaction between the regional and the international research communities and industry in the field. ; | en_US |
| dc.description.statementofresponsibility | edited by Shuvendu K. Lahiri, Chao Wang. | en_US |
| dc.description.tableofcontents | Formal Methods -- Verification -- Program Synthesis -- Model Checking -- Theorem Proving -- Software Verification -- SAT Solver -- SMT Solver -- Automaton Logic. ; | en_US |
| dc.format.extent | XIII, 560 p. 133 illus. ; online resource. ; | en_US |
| dc.publisher | Springer International Publishing : | en_US |
| dc.publisher | Imprint: Springer, | en_US |
| dc.relation.ispartofseries | Lecture Notes in Computer Science, ; 0302-9743 ; ; 11138. ; | en_US |
| dc.relation.ispartofseries | Lecture Notes in Computer Science, ; 0302-9743 ; ; 11138. ; | en_US |
| dc.relation.haspart | 9783030010898.pdf | en_US |
| dc.subject | Computer Science | en_US |
| dc.subject | Software Engineering | en_US |
| dc.subject | Programming Languages and Electronic Computers | en_US |
| dc.subject | Computer Security | en_US |
| dc.subject | Computer logic. ; | en_US |
| dc.subject | Mathematical logic. ; | en_US |
| dc.subject | Computer simulation. ; | en_US |
| dc.subject | Computer Science | en_US |
| dc.subject | Software Engineering | en_US |
| dc.subject | Programming Languages and Compilers and Interpreters | en_US |
| dc.subject | Systems and Data Security | en_US |
| dc.subject | Simulation and Modeling. ; | en_US |
| dc.subject | Logics and Meanings of Programs. ; | en_US |
| dc.subject | Mathematical Logic and Formal Languages. ; | en_US |
| dc.subject.lcc | QA76.758 ; | en_US |
| dc.title | Automated Technology for Verification and Analysis | en_US |
| dc.title.alternative | 16th International Symposium, ATVA 2018, Los Angeles, CA, USA, October 7-10, 2018, Proceedings / | en_US |
| dc.type | Book | en_US |
| dc.publisher.place | Cham : | en_US |
| مجموعه(های): | مدیریت فناوری اطلاعات | |
پیوست های این کاربرگه
| فایل | توضیحات | اندازه | فرمت | |
|---|---|---|---|---|
| 9783030010898.pdf | 19.14 MB | Adobe PDF | مشاهده فایل |